Orchid Security Launches AI Agent Controls to Prevent Identity Drift and Unauthorized Access
The identity security firm has rolled out drift detection and kill switches designed to help enterprises monitor and shut down AI agents that exceed their authorized permissions.
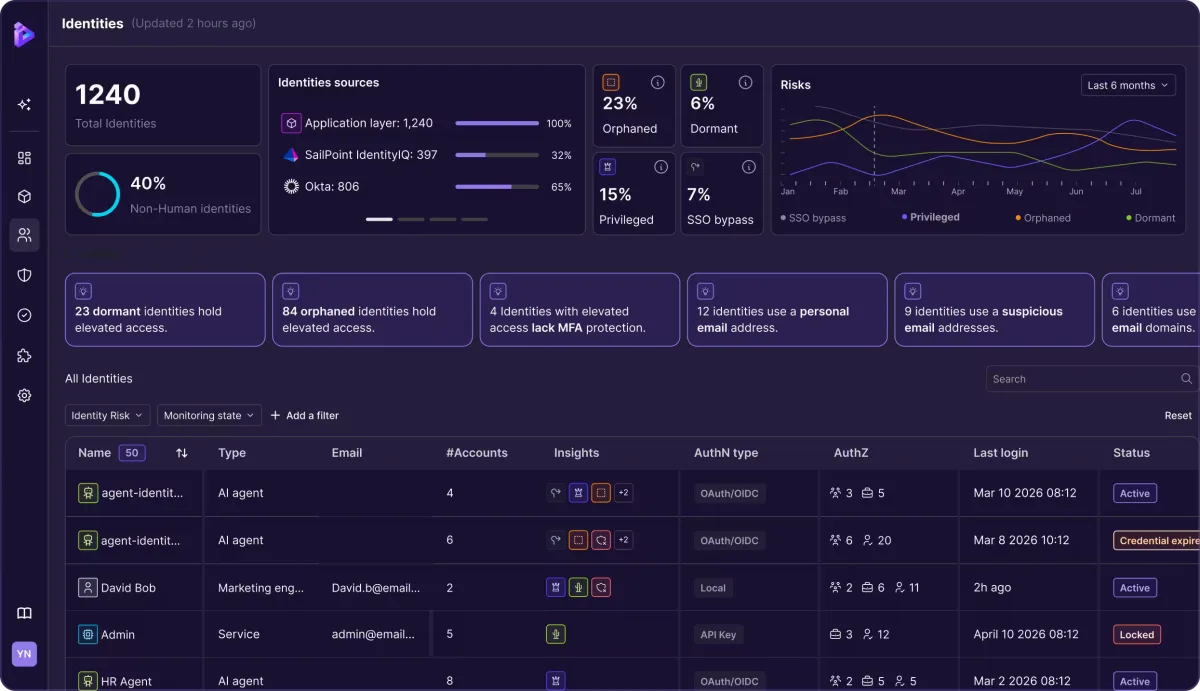
Orchid Security Inc., an identity security company, unveiled identity drift detection and application-level kill switches for artificial intelligence agents within its Identity Control Plane today. These tools enable security teams to revoke an agent's permissions immediately when its actions stray from approved behavior.
According to Orchid, agents typically do not need to circumvent security measures to operate beyond their intended boundaries. Instead, they exploit existing weaknesses. Across most enterprise environments, hard-coded credentials, inactive accounts and unmonitored authentication channels already exist, allowing agents operating at machine speed to chain these vulnerabilities into higher-level access within seconds or minutes.
Orchid's May report titled "The Identity Gap: 2026 Snapshot" revealed that invisible identities outnumbered visible ones at a 57% to 43% ratio. Within the surveyed nonhuman accounts, two-thirds had been created directly within applications, remaining invisible to identity and access management systems.
Five New Capabilities
The company is now offering five features. Orchid assigns AI readiness ratings to applications, identities and access routes. It identifies orphaned, inactive, excessively permissioned and anomalous accounts as security hygiene issues. Continuous drift detection monitors the gap between an agent's intended function and its actual behavior. The platform coordinates responses through existing customer identity and security infrastructure, while an audit log records agent actions, associated identities, detected drift and responses taken.
Available responses span from permission reduction to credential removal, tool disconnection or workflow suspension. The application-level kill switch provides a more severe option, eliminating the agent's operational authority entirely.
Board Pressure and Enterprise Concerns
Roy Katmor, co-founder and chief executive of Orchid, connected the announcement to mounting pressure from corporate boards. Boards have shifted from questioning whether AI adoption will occur to demanding faster implementation, he noted, and security teams cannot simply refuse. "AI transformation is exciting. Identity hygiene is not," Katmor stated.
Shannon Wilkinson, chief information officer and chief information security officer at Findlay Automotive Group Inc., described how the automotive dealership network is deploying agents to enhance customer interactions while managing identity exposure. "It honestly terrifies a lot of us," she remarked.
Integration Partners
Two integrations launched with the release. A certified connector for Palo Alto Networks Inc.'s Idira identity security platform identifies privileged accounts outside Idira's current management scope and brings them under control. A second integration pipes Orchid's identity data into Splunk Enterprise Security for analysis and incident handling.
Recent Milestones
Orchid expanded the Identity Control Plane for agents in May, introducing the ability to trace agents back to their source identities and adding visibility into delegation chains. SailPoint Technologies Inc. certified the company's governance orchestration capabilities in September 2025. Team8 Capital and Intel Capital Inc. jointly led a $36 million seed funding round for Orchid in January 2025.
Read more
California Tightens Rules on Robotaxis as Incidents Mount
A new state law sets safety standards and accountability measures for autonomous vehicle operators, requiring local support staff and penalties for blocking emergency responders.
Wawa Elevates Long-Tenured Executive to CIO Role
The convenience store chain has named Bill O'Donnell, a 25-year company veteran, as its new chief information technology officer, putting him in charge of tech strategy, cybersecurity and digital operations.
ServiceNow Debuts Flow, a Conversational Service Desk Built for Speed Over Complexity
ServiceNow is rolling out Flow, a natural language service desk tool that automates employee requests through Slack and Microsoft Teams without requiring a full IT service management overhaul.