Ransomware Operators Impersonate AI Tools to Infect Users, Cisco Talos Warns
Cybercriminals are creating counterfeit installers for popular AI services and manipulating search rankings to distribute three distinct ransomware variants, according to threat intelligence researchers at Cisco Talos.
Cisco Talos disclosed on Thursday that malicious actors are impersonating artificial intelligence platforms and vendors to deploy ransomware payloads. The threat intelligence division identified three separate malware campaigns: CyberLock, Lucky_Gh0$t, and Numero. Each exploits fraudulent software installers purporting to be legitimate AI applications, with attackers leveraging search engine optimization manipulation to elevate these malicious pages in organic search results.
CyberLock Exploits Fake NovaLeadsAI Portal
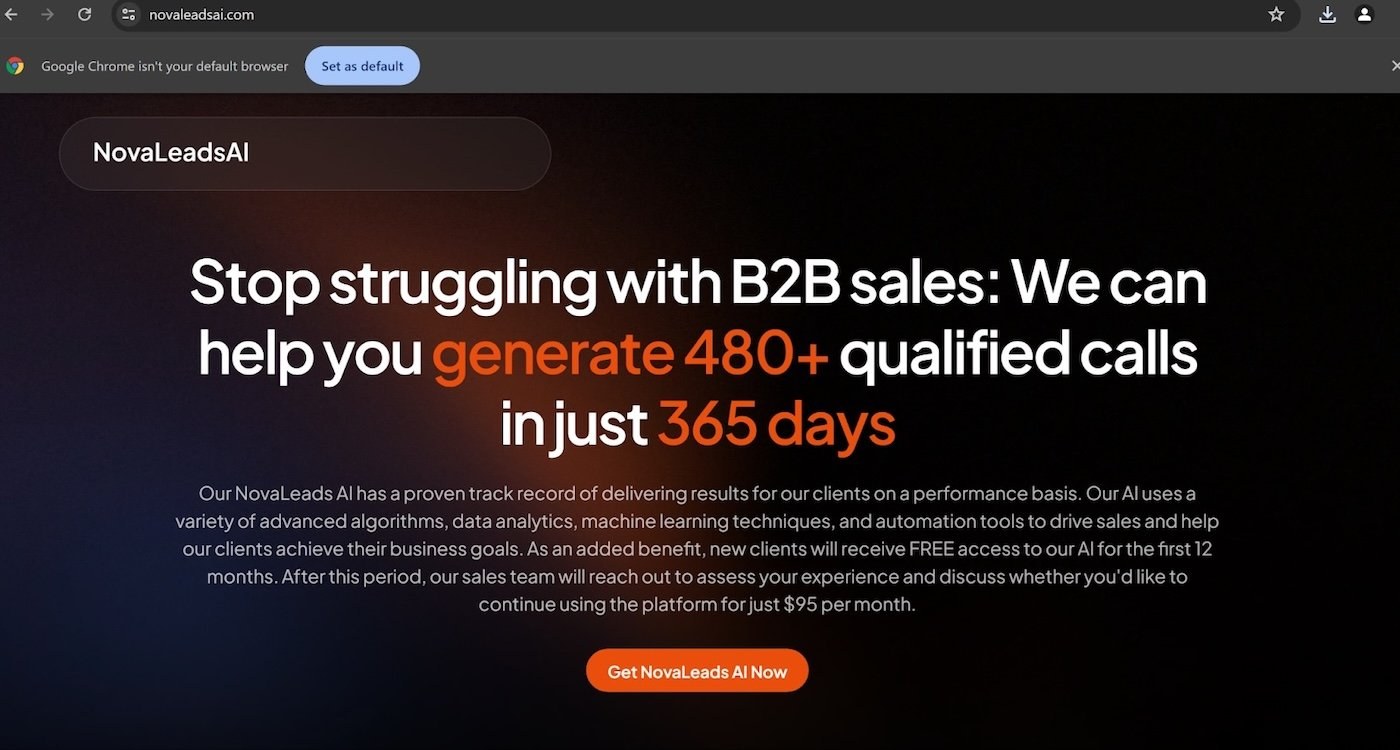
Attackers registered a deceptive domain mimicking NovaLeadsAI, a business-to-business lead generation platform. The fraudulent site employed a .com extension rather than the legitimate .app domain, and through SEO manipulation tactics, the counterfeit page achieved prominent placement in search engine results for relevant queries.
The CyberLock ransomware payload encrypts specific file types on infected systems. According to Cisco Talos, "The threat actors use a ransomware strain called CyberLock, which encrypts specific files on the user's device. If their device is infected, the user will see a message demanding a ransom in exchange for the return of their 'sensitive business documents, personal files and confidential databases.'"
The attackers demanded $50,000 in Monero cryptocurrency as ransom. To manipulate victims psychologically, they falsely claimed the funds would support humanitarian initiatives across Palestine, Ukraine, Africa, and Asia. While the threat actors threatened to publish encrypted files, Cisco Talos found no evidence that the ransomware contained actual data exfiltration capabilities.
Lucky_Gh0$t Masquerades as ChatGPT Download
The Lucky_Gh0$t ransomware presents itself as a complete version of ChatGPT through a file labeled "ChatGPT 4.0 full version – Premium.exe." In reality, the legitimate ChatGPT service operates entirely through a web browser and requires no installation. The malicious package bundles the ransomware executable alongside legitimate open-source Microsoft utilities designed for artificial intelligence development on Azure.
Upon execution, Lucky_Gh0$t encrypts numerous file formats spanning Microsoft Office documents, Adobe creative files, multimedia content, images, backup archives, and database files.
Numero Impersonates InVideo AI Service
A third malware variant called Numero mimics the InVideo AI online platform. The attack vector involves deceiving users into downloading a malicious file bearing the InVideo AI branding in its metadata. Installation deploys an executable file named 'wintitle.exe' alongside a malicious batch script and Visual Basic script. Cisco Talos published technical indicators of compromise through a GitHub repository for defensive purposes.
These campaigns underscore the importance of exercising caution when encountering download links, particularly those appearing at the top of search engine listings. Users and organizations should validate URLs, scrutinize website authenticity, and verify applications before installation. Cybersecurity researcher Chetan Raghuprasad stated: "Organizations and users must exercise extreme caution, meticulously verify sources, and rely exclusively on reputable vendors to avoid falling prey to these threats."
Read more

Identity governance faces new test as AI agents proliferate across enterprises
Autonomous AI agents are forcing organizations to rethink how they manage access and permissions at machine speed. SailPoint's Navigate conference will explore how identity security must evolve to handle this expanding population of non-human actors.

Vertical AI and Purpose-Built Hardware Drive Next Wave of Technology Growth
Specialized AI systems tailored to specific industries are emerging as the primary engine for the next phase of technology expansion, according to insights from the Bank of America Private Tech Trailblazers Conference 2026.

CrowdStrike and CoreWeave Partner to Automate AI Security at Machine Speed
As cyberattackers breach systems in seconds, CrowdStrike and CoreWeave are embedding automated defenses throughout AI infrastructure, turning attacks into training data for faster response.