LGT Financial Services Tests Post-Quantum Cryptography in Live Banking System
A Swiss financial services firm has begun migrating to quantum-safe cryptography by treating the transition as a series of coordinated waves rather than a single project, with its online banking system now running hybrid key exchange in production.
Managing a shift to post-quantum cryptography becomes overwhelming if organizations approach each cryptographic dependency as an isolated replacement effort. The migration from theoretical quantum risk to practical deployment spans applications, infrastructure and third-party vendors, requiring orchestration across teams as much as technical algorithm choices.
LGT Financial Services AG brought quantum safety into its formal risk framework in 2022, when the subject surfaced during the company's annual risk and cyber risk management session. The organization subsequently established a competence center to unite security operations, infrastructure teams, public key infrastructure specialists, application owners, external suppliers and risk management personnel, according to Christian Pfister, team leader for IT security operations and head of LGT's Quantum Safe Competence Center.
Quantum safety is a resilience and risk management issue. The key question for leadership was straightforward: Which information must remain confidential long enough that it may be exposed to a future cryptographic break? We then explained that waiting until there is a cryptographically relevant quantum computer would leave too little time to identify dependencies, upgrade product, coordinate suppliers and safely migrate.
Christian Pfister
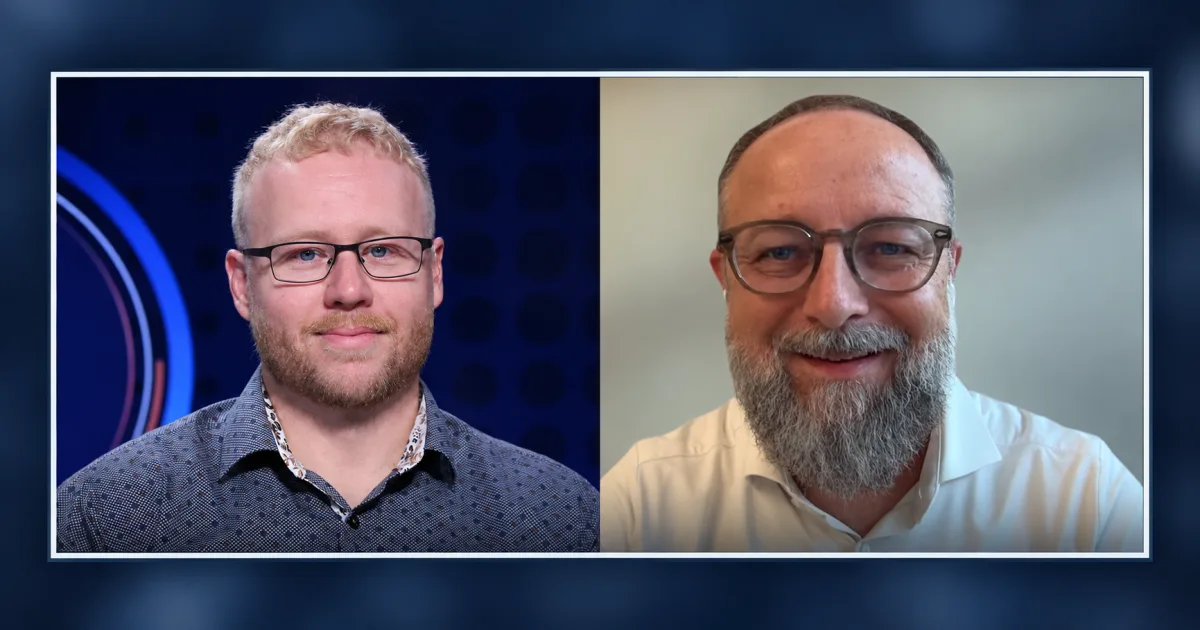
Pfister discussed LGT's approach with Shane Kelly, principal crypto architect at DigiCert Inc., during DigiCert's World Quantum Readiness Day event, in remarks broadcast on theCUBE, SiliconANGLE Media's livestreaming platform. The conversation covered LGT's migration strategy, initial technical implementations and takeaways for organizations starting similar transitions.
Phased approach replaces single-project model
The competence center sets security policy direction, while individual teams and service owners execute the actual migration work. This separation enabled LGT to launch focused initiatives while simultaneously building out a complete inventory of cryptographic dependencies, Pfister explained.
If you try to inventory, replace and validate every cryptographic use case at once, it makes the program unmanageable, and you can't measure the outcome. The [post-quantum cryptography] migration is not one project and one algorithm change; it's a series of migration waves.
Christian Pfister
Engaging with suppliers formed a separate workstream that involved vendor management and procurement functions. Starting in 2023 or 2024, LGT began requesting information from vendors regarding product development plans, algorithm support, implementation timelines and technical constraints, according to Pfister.
That vendor management, it seems now a very important part. Therefore, we got connections — connections to DigiCert, to experts to talk with. That was also a very important part [that] we coordinated with the Quantum Safe Competence Center.
Christian Pfister
Hybrid key exchange deployment reveals infrastructure gaps
LGT's technical work began by upgrading its Transport Layer Security configuration and running hybrid key exchange trials in isolated test environments, Pfister noted. The testing combined X25519 with the NIST-standardized Module-Lattice-Based Key-Encapsulation Mechanism, pairing a conventional key exchange with a post-quantum alternative.
This pilot is now live, and our online banking system uses hybrid key exchange, and our customers don't have any disruption. This principle we are going to follow in all areas.
Christian Pfister
The pilot uncovered interoperability challenges throughout the entire connection infrastructure, encompassing load balancers and content delivery networks. Certain connections encountered failures or reverted to earlier configurations, demonstrating the necessity for comprehensive testing across the full stack rather than examining individual components in isolation, Pfister noted.
Most issues look familiar to anyone who has delivered major security changes. We are all familiar with legacy hardware, unsupported firmware [and] unmanaged libraries. The [pilot] exposes technical debt that already exists, and that's not the reason to wait. It's precisely why starting early matters for us.
Christian Pfister
Read more

Identity governance faces new test as AI agents proliferate across enterprises
Autonomous AI agents are forcing organizations to rethink how they manage access and permissions at machine speed. SailPoint's Navigate conference will explore how identity security must evolve to handle this expanding population of non-human actors.

Vertical AI and Purpose-Built Hardware Drive Next Wave of Technology Growth
Specialized AI systems tailored to specific industries are emerging as the primary engine for the next phase of technology expansion, according to insights from the Bank of America Private Tech Trailblazers Conference 2026.

CrowdStrike and CoreWeave Partner to Automate AI Security at Machine Speed
As cyberattackers breach systems in seconds, CrowdStrike and CoreWeave are embedding automated defenses throughout AI infrastructure, turning attacks into training data for faster response.