Dell positions supply chain vetting as foundation for securing autonomous AI agents
As enterprises deploy AI agents capable of independent action, Dell Technologies argues that supply chain security and layered defenses must anchor protection strategies that legacy tools cannot provide.
Integrating artificial intelligence into mission-critical business functions is reshaping how organizations think about security. The introduction of these systems creates fresh vulnerabilities that demand careful scrutiny of how computing resources, information assets and self-directed software are safeguarded.
The emergence of AI agents capable of autonomous decision-making is forcing a reassessment of where vulnerabilities originate and who bears responsibility for managing them. Dell Technologies has positioned AI factory security as a cornerstone of this evolving conversation. Kamlesh Shah, director of product management for Dell AI Factory Solutions at Dell, emphasized the urgency: "With the speed and scale at which the AI systems are growing, the enterprise needs to be ready to be able to actually act at [that] speed and scale. And it doesn't happen overnight."
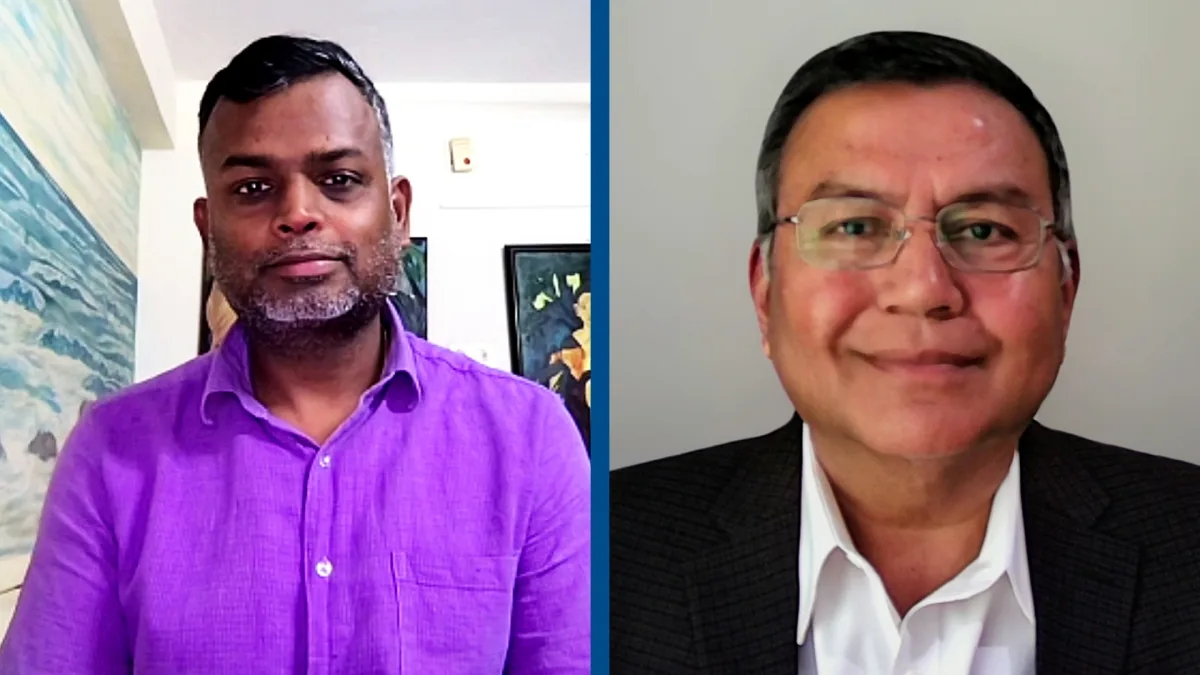
Shah and Ash Lakshmanan, director of product management for Dell Services at Dell, shared their perspective during an exclusive conversation with theCUBE Research's Dave Vellante at the AI Cybersecurity and Resilience Summit, broadcast through theCUBE, SiliconANGLE Media's streaming platform.
Supply chain security anchors a layered AI defense
Dell's security framework relies on approaches that security professionals already recognize. The foundation rests on supply chain security, which involves evaluating vendors before product development begins and maintaining protective measures throughout the entire deployment lifecycle, according to Shah. The company has delivered these capabilities through its Dell AI Factory offering while simultaneously implementing them across its own internal technology infrastructure.
Shah noted that "Dell's experience in the AI infrastructure as a provider and a very large-scale AI user has created a model that the customers can look at and replicate. The goal is to turn these deployment lessons into repeatable patterns … rather than reinvent the control."
Autonomous agents introduce a fundamentally different risk profile compared to traditional systems. Unlike tools designed merely to respond to queries, agents operate toward defined objectives by executing sequences of actions, locating and leveraging external tools, accessing backend systems and coordinating with other agents. This expanded capability makes their actions harder to predict, Shah explained. Managing this unpredictability requires strict guardrails: validation of policies at runtime, isolated execution environments and comprehensive logging of authorization decisions.
Shah stressed that "The agent itself should have the ability and identity that's tied to a particular workload, not a broad-based permission to work on all applications. The layer at which the agent needs to operate is really delegated, narrowly scoped permissions. Time-based."
After organizations settle on an architecture, Dell Services assists in converting experimental use cases into production-ready systems that can be managed, controlled and refined over time, according to Lakshmanan. This engagement addresses security across four interconnected layers: hardware, runtime, data and applications. The dimension that organizations frequently overlook is comprehensive visibility spanning all four layers, he noted.
Lakshmanan observed that "Your old tools just cannot look at AI workloads. Your old tools that could look at human identities and possibly machine identities cannot look at agent identities."
Several organizations that engaged Dell's penetration testing services to evaluate chatbots before public release discovered critical vulnerabilities that could have enabled attackers to compromise the systems, according to Lakshmanan. Dell is collaborating with Nvidia Corp. to extend agentic AI capabilities from individual workstations into enterprise data centers.
https://www.youtube.com/embed/jJrBF9GvD8Y?feature=oembed
Lakshmanan concluded that "We need new tools, platforms and skills to tackle this. But the foundational elements of security have not gone away, which is the layered security approach we talked about. You still need to narrow your attack surface. You still need 24/7 continuous observability, and you need to be prepared as if a breach could happen."
Read more
AI infrastructure shifts from raw compute to systems thinking: 11 takeaways from CASPA's CEO Summit
The era of competing on processor speed alone has ended. As hundreds of thousands of chips now operate as unified systems, the industry's focus is turning to interconnects, memory, power and the bottlenecks that surround the processor itself.
Cloudera Positions Portability as the Key to Enterprise AI, Not Agent Features Alone
As enterprises demand greater control over AI workloads amid regulatory concerns and vendor lock-in fears, Cloudera is betting that the ability to run models anywhere—across clouds and on-premises—will matter more than general-purpose AI agents.
Regal Voice Launches Dual-Model Agents to Streamline Enterprise Call Handling
The enterprise voice AI company has introduced Goal Oriented Agents, a system that deploys two specialized models on each call to manage conversation flow and track business objectives more efficiently.