Identity Security Must Adapt as AI Agents Operate Across Enterprise Systems
Okta's Oktane event revealed that securing AI agents requires shared architecture, cross-vendor cooperation and runtime controls that extend identity management beyond initial login.
Identity security is shifting from a perimeter-based model to something embedded in the operational flow of AI agents. When autonomous agents invoke tools, hand off work and move between applications, enterprises must enforce controls that track and govern those actions throughout their lifecycle, not just at the point of initial access. The core challenge lies in maintaining these safeguards across disparate systems without disrupting the business processes that agents enable.
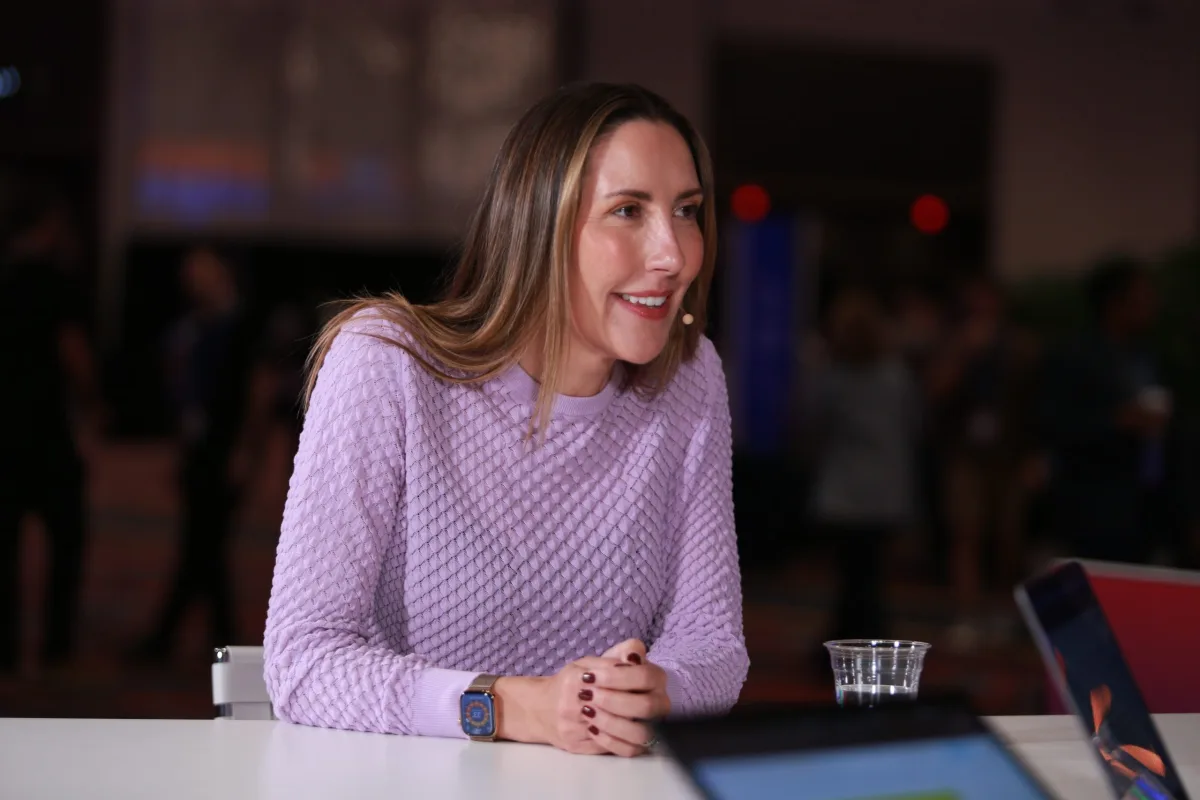
During Okta Inc.'s Oktane event, the constraints of single-vendor security platforms surfaced repeatedly as a key concern. When agents operate across interconnected systems, the questions enterprises face go far beyond simple access grants or revocations. Krista Case, principal analyst at theCUBE Research, highlighted a critical gap: "What I am interested to see as it gets rolled out and as we start to talk with customers about it is if there are conflicting insights across these platforms about an action that needs to be taken. For example, who is going to have the authority at the end of the day, and where is that authority going to live in this tech stack?"
https://www.youtube.com/embed/Wea55Yw3dWU?feature=oembed
Shared Architecture and Inline Controls Are Essential
Securing agents across multiple applications demands that security platforms operate from a common reference architecture. The Blueprint Alliance brings together multiple vendors around a unified framework designed to help organizations protect their agent environments. Charlotte Wylie, senior vice president and deputy chief security officer of Okta, explained the industry's shift in approach: "Rather than trying to solve that problem alone, there is a recognition that we have to galvanize as an industry to solve this problem for our customers at a speed that they are scrambling to run after. We want to make sure that we provide an architecture, a referenceable position [for] how to use the technology that we all offer in a way that we can secure the entire agentic stack."
Beyond shared architecture, enterprises need a runtime checkpoint where controls can evaluate and authorize agent actions before they execute. Okta's Agent Gateway represents a significant expansion of the identity provider's traditional role. Rather than simply granting access credentials, the platform now operates inline to make authorization decisions about what agents attempt to do. Ric Smith, president of products and technology at Okta, described the shift: "That is a very different transition for Okta. We had not been inline, so with us moving in that direction, it means that we can do a lot more decision-making in terms of what we authorize."
Within Okta itself, the company has deployed Dex, a platform that provides employees with access to specialized agents while keeping interface complexity manageable. Jenna Cline, senior vice president of technology, data and intelligence at Okta, described how the system works: "Dex can call upon the right sub-agent. That agent is scoped to only work on certain things, so it's very secure, and it's very efficient because it does one thing really well. But Dex can do that for other agents; it can do that for the expense team [and] it can do that for our IT help desk."
https://www.youtube.com/embed/g323e3AFrLg?feature=oembed
Cross-Vendor Cooperation Is Mandatory
Effective agent governance depends on access decisions and authorization context flowing reliably across vendor boundaries. Okta and AgileBits Inc., which operates as 1Password, have aligned around shared identity standards to maintain an agent's verified identity and authorization state as it moves between systems. 1Password's Credential Broker allows agents to access secrets without exposing them to the agent itself or to the underlying model. Nancy Wang, chief technology officer of 1Password, drew a parallel to human workforce management: "Just like you would verify whatever an intern does before you allow them to move on to the next project, [it's the] same thing with agents. You just want that agent to prove that it actually finished its last task with the right level of permissions, doing the right thing before you allow it to move on to the next task."
Cooperation becomes equally critical when an agent's behavior deviates and requires containment. ServiceNow Inc. maps agents to the business processes they support and is collaborating with Okta on agent identities and session tokens. These connections enable more informed decisions about when and how to isolate an agent if needed. Bhakti Pitre, vice president of AI platform security product at ServiceNow, emphasized the necessity of industry-wide alignment: "Everybody in the industry needs to come together and be each other's friends or frenemies. If the AI needs to be at the scale where it is democratized for every person to use it, then every vendor needs to come together and play their part."
https://www.youtube.com/embed/Q4Dg0Q1CMqo?feature=oembed
Simplified Infrastructure and Existing Governance Frameworks Provide a Foundation
Organizations that have already moved away from traditional infrastructure layers find themselves better positioned to support agent deployments. The Professional Golfers' Association of America has eliminated data centers and corporate networks from its architecture, relying instead on Okta and Auth0. This approach frees resources for technology investments that directly serve members and customers. Kevin Scott, chief technology officer of the PGA of America, explained the rationale: "We don't have much of a team — it's small, it is lean. I don't mean to be reductive, but if we were to spend half of the technology budget on administering systems, none of our customers are ever going to come along and say, 'Thank you for that.'"
https://www.youtube.com/embed/UIth8O-mdM8?feature=oembed
At Vanderbilt University, the focus is on extending established governance processes to cover agent identities. The institution uses OneVU, powered by Okta, for single sign-on and is evaluating how its institutional oversight mechanisms should adapt to this new category of identity. Shane Callahan, chief information officer of Vanderbilt, argued against treating agent governance as a separate problem: "We're treating AI like it's a brand-new thing. But really, you're still talking about identity data in another technology tool. You don't have to recreate everything. If you have a governance process and a technology intake program, do that, use that."
https://www.youtube.com/embed/videoseries?list=PLNvsT8kNEPNE
Read more
Moonshot AI Unveils Kimi K3.1 Pro, a 3-Trillion-Parameter Model Rivaling OpenAI and Anthropic
The Chinese AI firm has released an upgraded version of its Kimi K3 model that matches or exceeds competitors in several specialized tasks, particularly 3D modeling and financial analysis.
Managed Services Become Critical to Neocloud Success as GPU Providers Scale
Smaller AI infrastructure providers are increasingly relying on hardware partner support to keep their GPU clusters operational and profitable after launch, with managed services becoming a key differentiator in the competitive neocloud market.
Why AI ROI Remains Elusive: Breaking Out of the Productivity Trap
Companies are discovering that deploying AI tools in isolation—without overhauling the business processes around them—delivers disappointing returns. The gap between hype and reality is what some call AI's "valley of despair."